Sample report
What SSLBoard found on airbus.com
This is the report a paying customer receives, run on a domain we have no relationship with. We gave SSLBoard the name airbus.com and nothing else. It found 1,393 hostnames, tested 1,318 endpoints, and turned the results into 20 actions in the order they should be done.
45 pages · 305 KB · scanned 5 November 2026
Scanned domain
airbus.com
2026-11-05 05:37 UTC
1,393 hostnames · 1,318 endpoints
Critical
95% of similar-size scans score higher
3
Fix now
10
Fix soon
7
Review
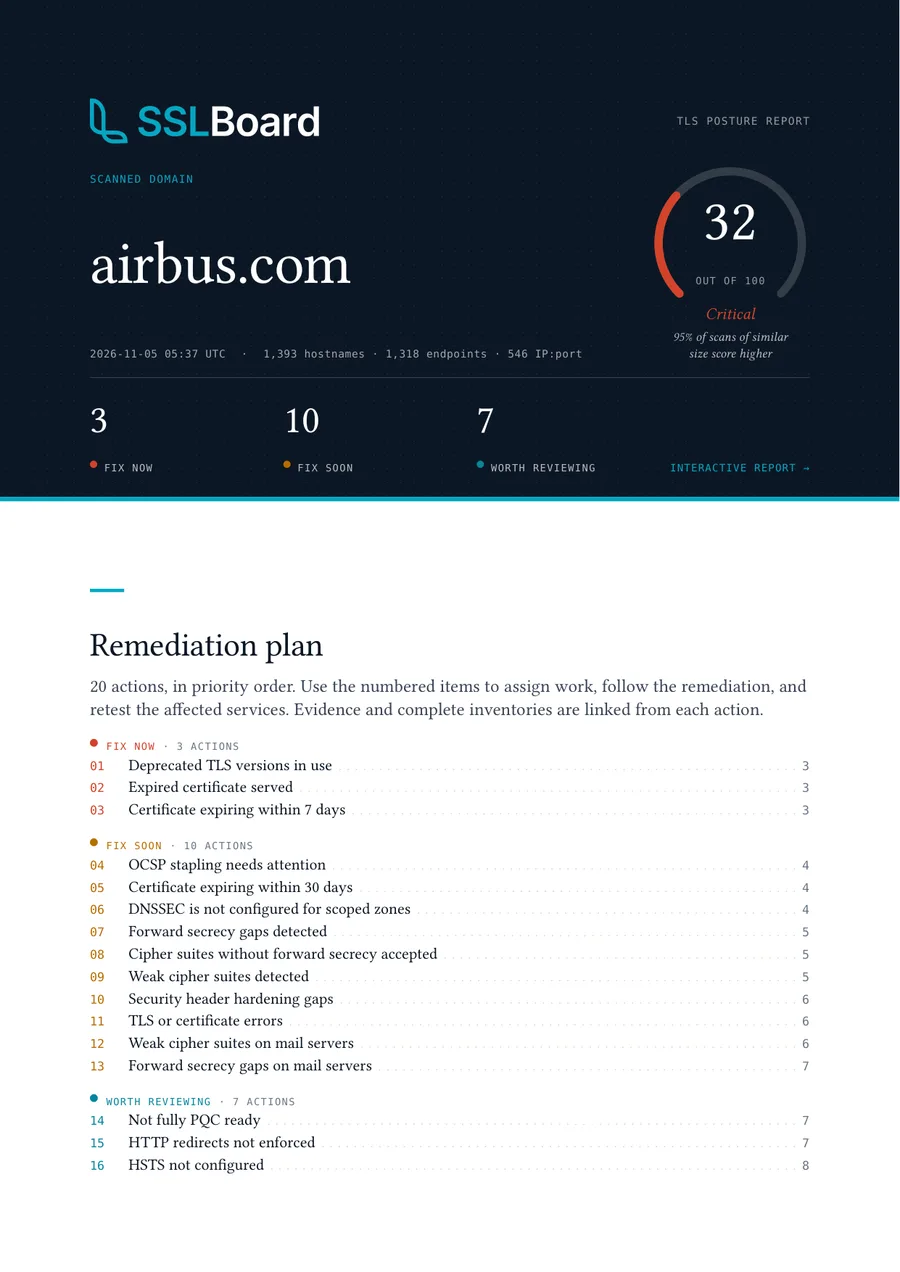
The remediation plan comes first
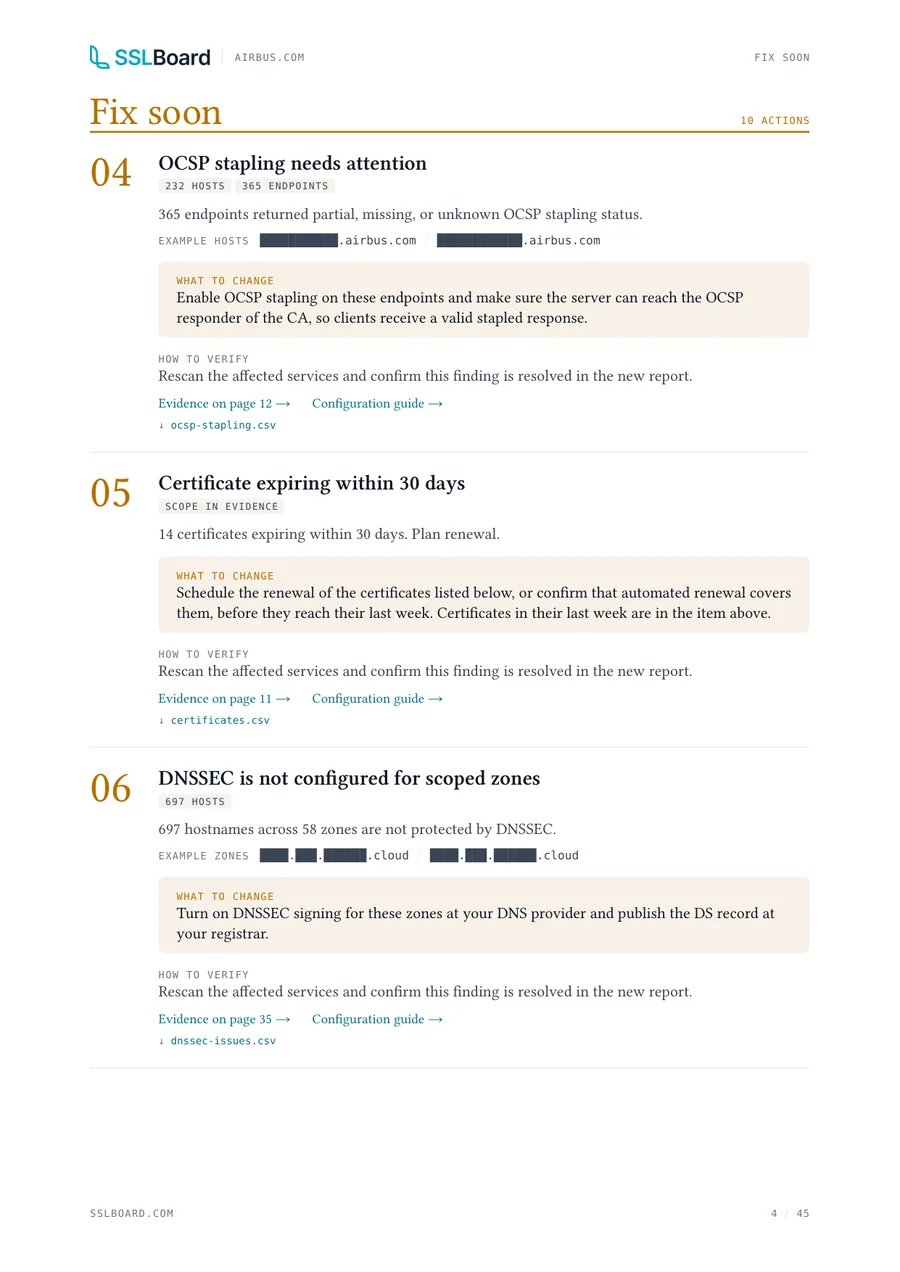
Page one is a to-do list, not a dashboard. Each action is numbered so it can be assigned, and each one links to what to change, how to verify it, the evidence, and a CSV of the affected hosts.
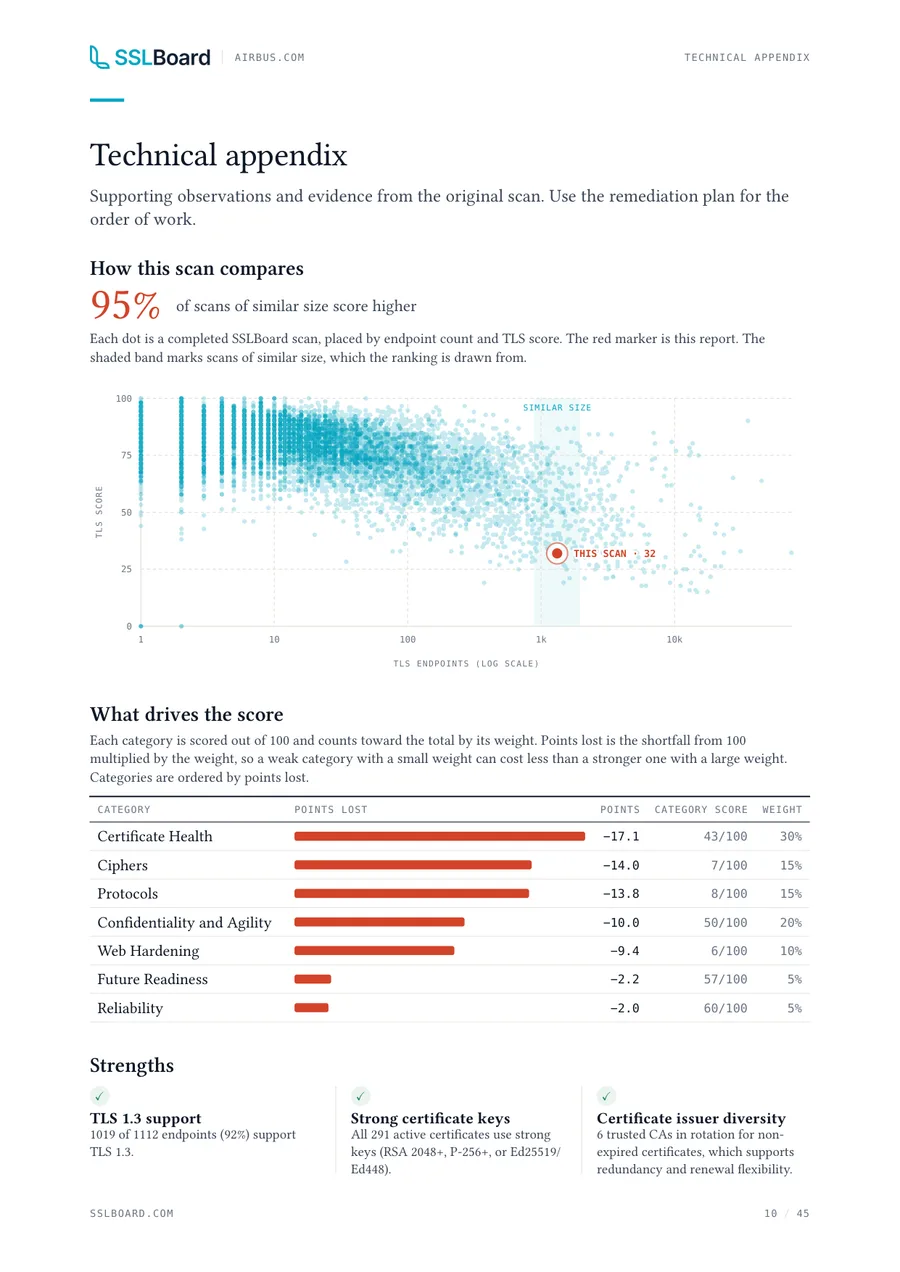
The score explains the urgency. At 32 out of 100, airbus.com sits below 95% of SSLBoard scans of a similar size.
Fix now · 3 actions
- 01 Deprecated TLS versions in use
- 02 Expired certificate served
- 03 Certificate expiring within 7 days
Fix soon · 10 actions
- 04 OCSP stapling needs attention
- 05 Certificate expiring within 30 days
- 06 DNSSEC is not configured for scoped zones
- 07 Forward secrecy gaps detected
- 08 Cipher suites without forward secrecy accepted
- 09 Weak cipher suites detected
- 10 Security header hardening gaps
- 11 TLS or certificate errors
- 12 Weak cipher suites on mail servers
- 13 Forward secrecy gaps on mail servers
Worth reviewing · 7 actions
- 14 Not fully PQC ready
- 15 HTTP redirects not enforced
- 16 HSTS not configured
- 17 RSA-only hosts
- 18 Unreachable endpoints
- 19 TLS 1.2 forward secrecy not confirmed on mail servers
- 20 Mail servers not PQC ready
Every action says what to do
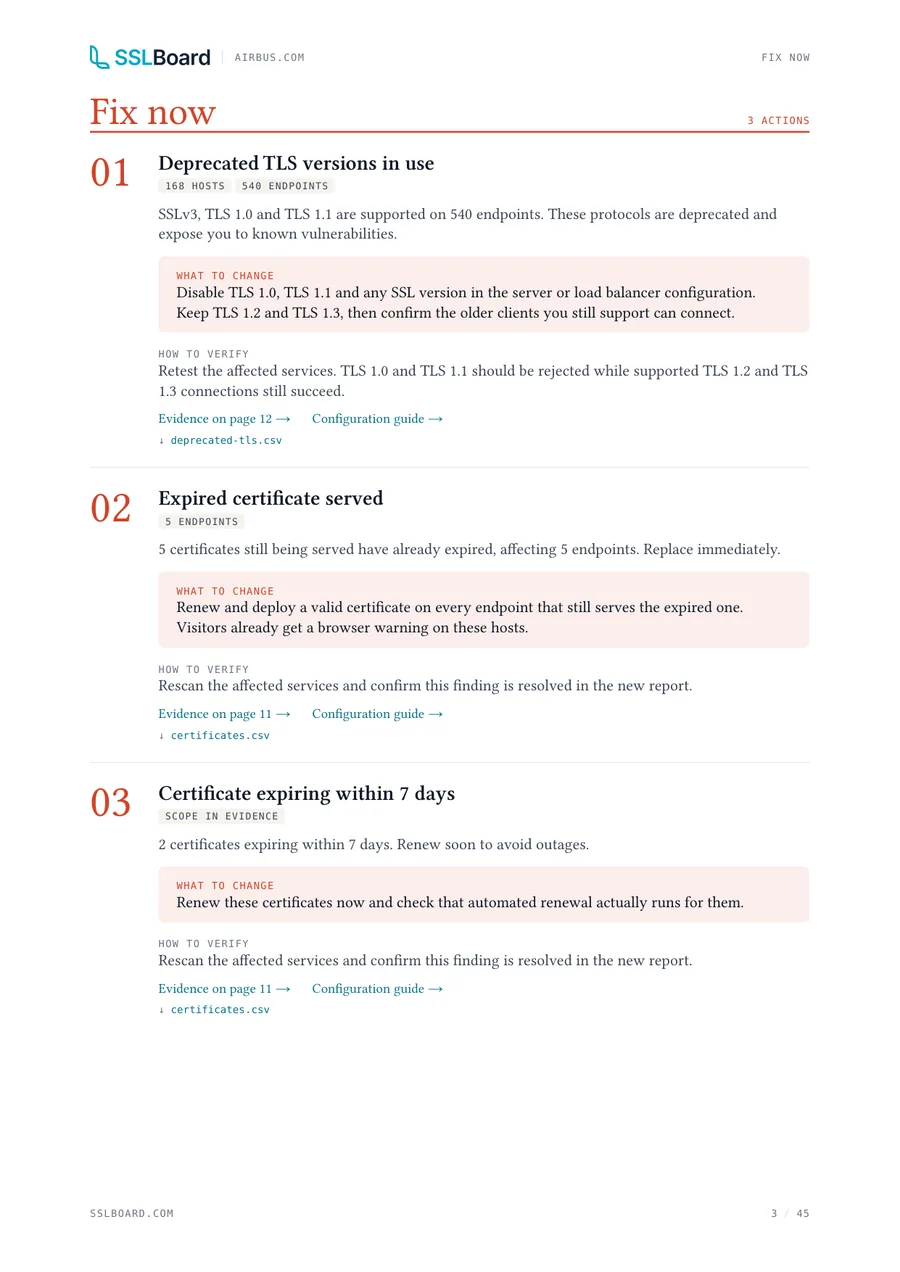
Findings are written for the person who will make the change. This is action 01, as it appears on page 3.
Deprecated TLS versions in use
168 hosts 540 endpoints
SSLv3, TLS 1.0 and TLS 1.1 are supported on 540 endpoints. These protocols are deprecated and expose you to known vulnerabilities.
What to change
Disable TLS 1.0, TLS 1.1 and any SSL version in the server or load balancer configuration. Keep TLS 1.2 and TLS 1.3, then confirm the older clients you still support can connect.
How to verify
Retest the affected services. TLS 1.0 and TLS 1.1 should be rejected while TLS 1.2 and TLS 1.3 connections still succeed.
Then the evidence, in 11 sections
The technical appendix backs every action with the hosts, IP addresses and ports involved. Here is one figure from each section.
- 1
Certificates
5 expired certificates still served, 2 more expiring within a week and 14 within a month.
- 2
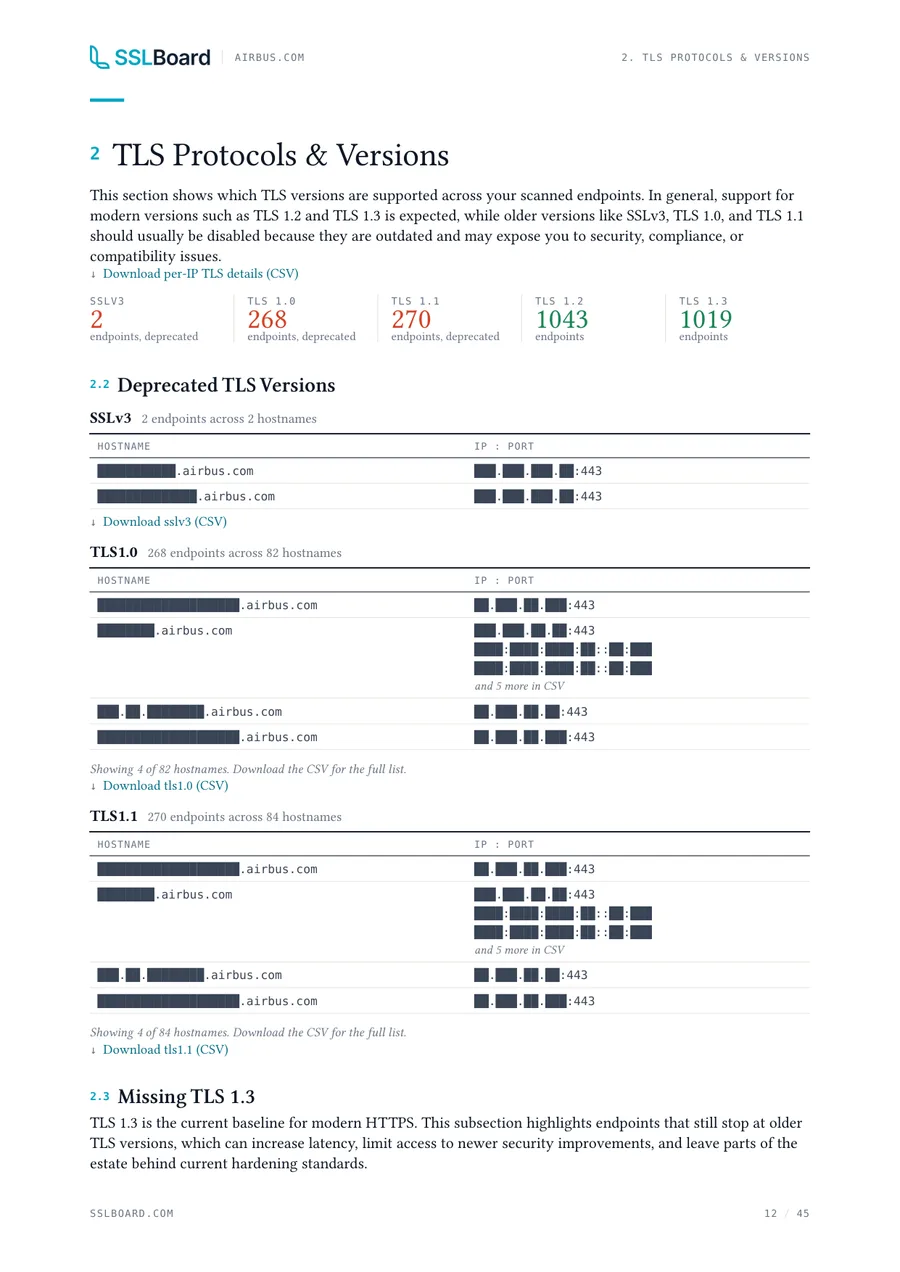
TLS protocols and versions
268 endpoints accept TLS 1.0, 270 accept TLS 1.1 and 2 still answer on SSLv3. TLS 1.3 runs on 1,019 of 1,112.
- 3
Weak cipher suites
1 endpoint still offers an export-grade RC4 suite from the 1990s, next to hundreds using static RSA key exchange.
- 4
Forward secrecy
167 hosts accept cipher suites without forward secrecy, and 7 have none at all.
- 5
Key analysis
76% of certificates use RSA 2048. All 291 active certificates use keys of acceptable strength.
- 6
Redirects and security headers
450/610 hostnames send HSTS. Only 137 of 482 send a Content Security Policy.
- 7
Connection and certificate errors
172 hostnames refuse the connection or time out, which often points to stale DNS records.
- 8
Post-quantum readiness
83% of 1,009 endpoints negotiate hybrid X25519MLKEM768 key exchange.
- 9
DNSSEC
58 zones are unsigned, 6 are secure and 4 return validation errors.
- 10
Email security
0 MTA-STS or TLS-RPT policies published for the domain's two MX hosts.
- 11
Adjacent domains
192 other apex domains appear on the same certificates, which maps the wider estate.
Get the same report for your domain
The scan and the summary are free. The full report with the PDF, the remediation plan and 30 days of retests is paid once: $9 for up to 15 endpoints, $49 for larger estates.
Airbus is not an SSLBoard customer and did not request or review this report. It was produced on 5 November 2026 from public sources only: DNS, Certificate Transparency logs and standard TLS, HTTP and SMTP connections. Results describe what was observable on that date.